- infoblox:blogs/category/cloud
New Spam Actor: EggshellCheetah
EggshellCheetah is the actor behind the high-volume spam campaigns that send emails with links to sites that pose as legitimate.
Author: Maël LaTouz
Executive Summary
EggshellCheetah is the actor behind the high-volume spam campaigns that send emails with links to sites that pose as legitimate. EggshellCheetah aims to collect financial information, sell counterfeit products, and disseminate malspam supporting other actors’ scams. The actor’s campaigns employ a variety of lure topics, many of which have political themes. We do not know whether the actor itself or the actors it supports use malware.
Characteristics of Spam Campaigns
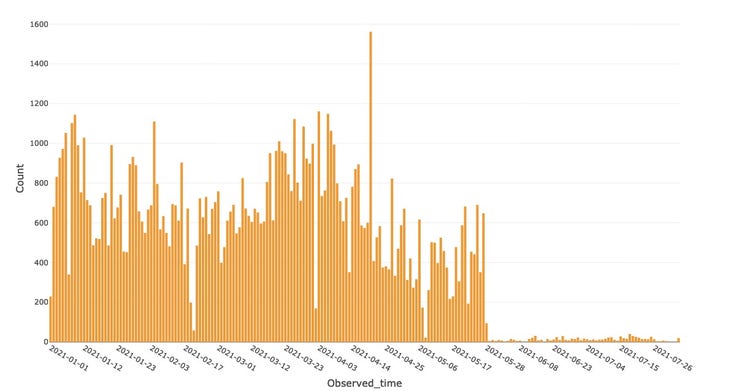
The actor’s typical campaign covers topics in healthcare and politics, and it often reuses language from other campaigns. Since the end of 2020, the actor has been running campaigns several times each week, and the number of emails has been extremely high. However, that number has decreased in the months leading up to this report (see Figure 1); we cannot confirm whether the actor has simply ceased its activity or changed its behavior or infrastructure.
Some of EggshellCheetah’s landing pages mention an Indian company that, as the actor claims, specializes in email marketing. We have observed that the actor’s campaigns have targeted U.S. residents in general and, on some occasions, various voting demographics. The emails’ subject lines often mention current events, such as Black Lives Matter protests, the presidential election, and debates on gun rights. The actor has also advertised “bait” items for purchase, such as VirtualPilot3D, gun holsters, and counterfeit medications.
Figure 1: The number of emails distributed by EggshellCheetah in 2021
Attack Chain
EggshellCheetah uses its own infrastructure for its campaigns. After clicking a URL within the body of the malspam email, the victim is taken to a landing page that triggers other redirects until the victim comes to a landing page on an attacker-controlled domain. In most cases, EggshellCheetah uses a pop-up that offers a fake unsubscribe button and an email address for complaints. The victim is then taken to another landing page, which offers a product and asks the victim to provide personal and banking information to complete the purchase.
Conclusion, Recommendations, and Mitigation
EggshellCheetah seems to be motivated financially first and foremost. Also, so far, EggshellCheetah has left no evidence of malware activity. The following recommendations should help users avoid falling victim to EggshellCheetah and other phishing and malspam-related threats:
- Be suspicious of vague or empty emails, especially those with prompts to open attachments or click URLs or hyperlinked text.
- Be suspicious of emails that come from unfamiliar sources, and never click URLs in such messages.
- Be suspicious of emails that discuss financial topics or contain delivery instructions.
- Inspect all attachments before opening them.
- Avoid opening emails with generic subject lines.